


Risk management and asset inventory for ISO 27001 and ENS
Keep a risk register where every risk has an owner, a treatment decision and a residual level at each review, built on an inventory of everything you need to protect.
From your assets to treated risks
Risks are assessed on the assets in your inventory, treated with the controls of your frameworks and reviewed over time.
Asset inventory
Information, processes, software, hardware, people, facilities and suppliers, each with an owner and a criticality rating.
Risk assessment
Describe what could happen to those assets and rate likelihood and impact from 1 to 5.
Treatment and safeguards
Mitigate or accept each risk and link the safeguards to your ISO 27001 or ENS controls.
Review
Reassess residual risk at each review and compare it with previous periods.
Risk register and heatmap
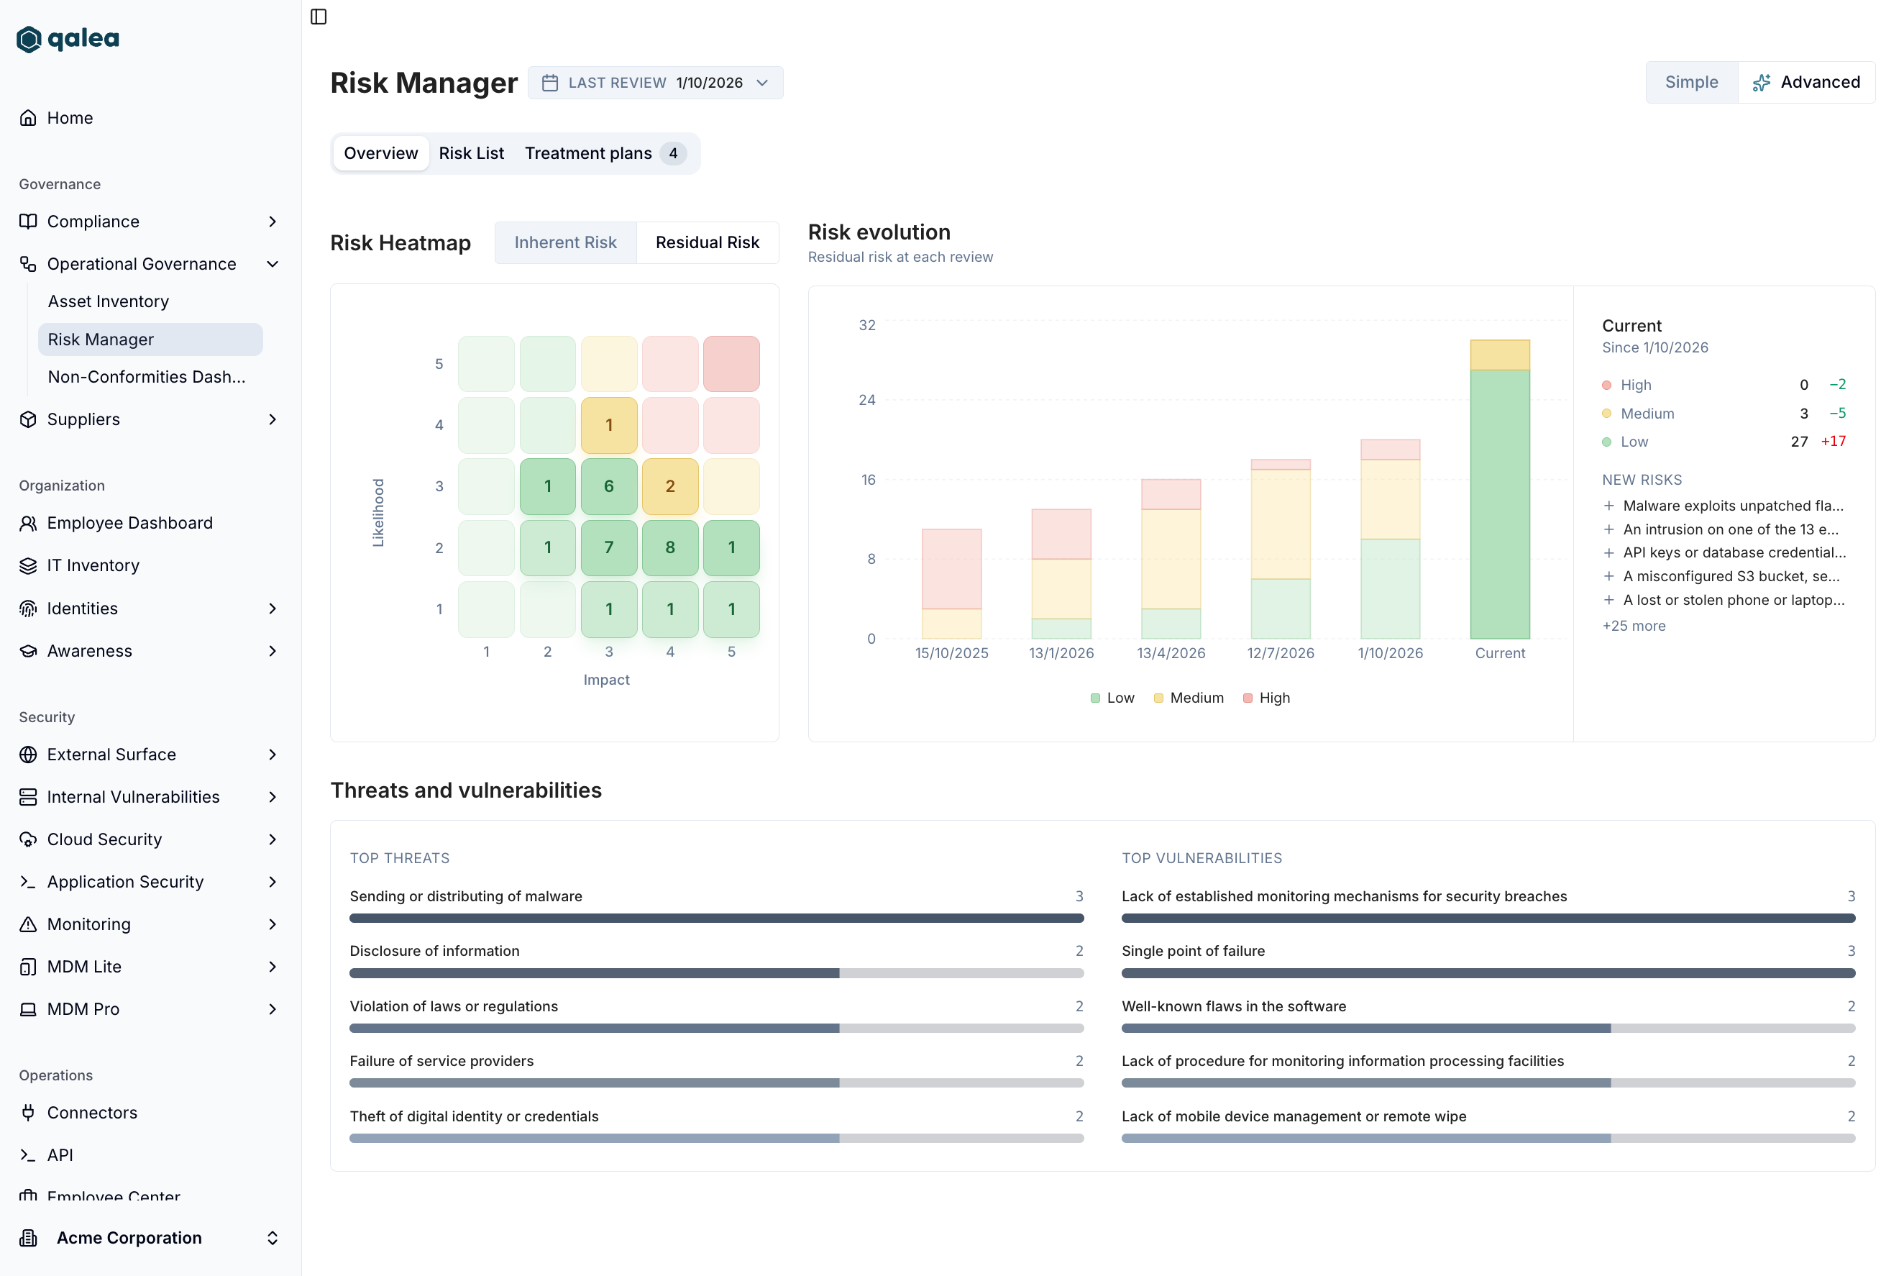
Every risk is evaluated twice: before safeguards, as inherent risk, and after them, as residual risk.
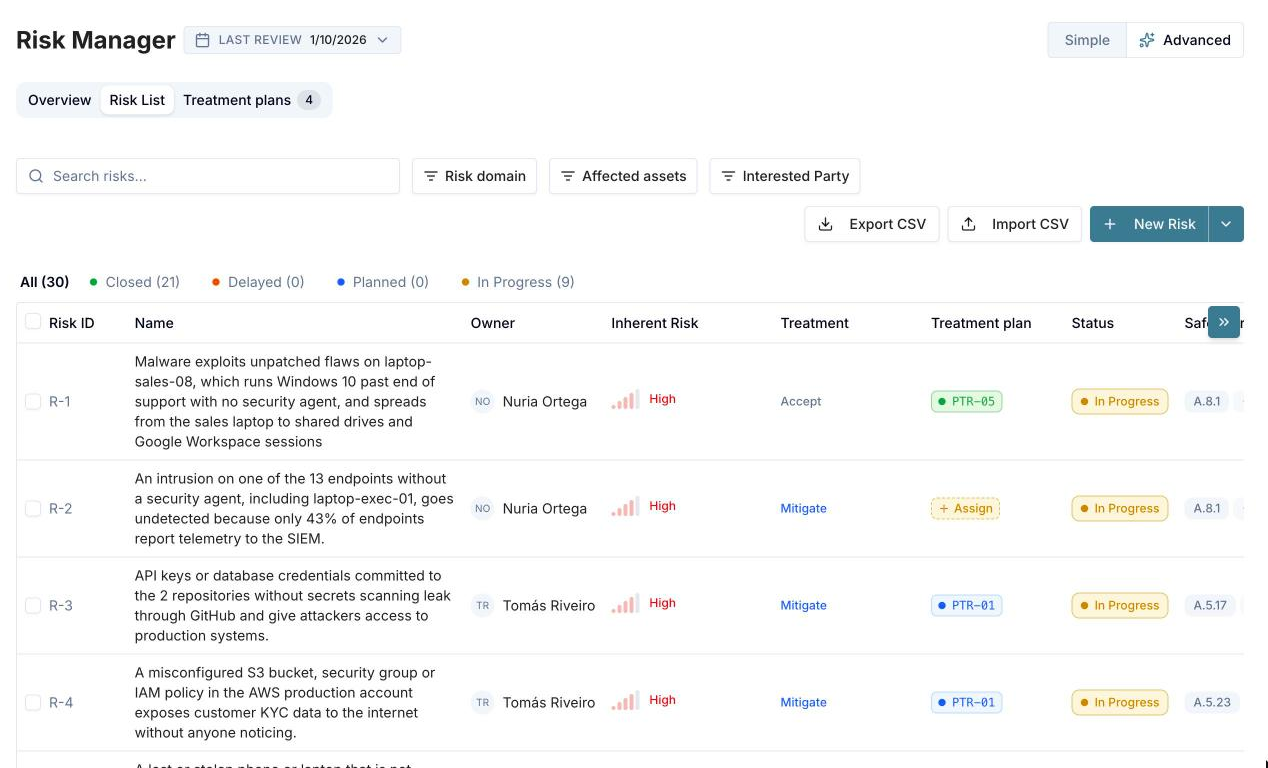
Risk register with owners
Each risk has an owner, the assets it affects, the interested parties and a status: planned, in progress, delayed or closed. Import and export the register in CSV.
Inherent and residual heatmap
A 5×5 heatmap of likelihood and impact, with a toggle between inherent and residual risk.
Treatment and safeguards
Mitigate or accept each risk, describe the measures, link them to ISO 27001 or ENS controls and rate their effectiveness from 1 to 5.
Risk catalogue based on ISO 27005
Add predefined scenarios filtered by asset type, with threats, vulnerabilities and impacted dimensions already filled in, then adapt them to your company.
Reviews and evolution
See the register as it stood at any previous review, how residual risk evolves from one review to the next, and every change with its date and author.
A methodology that fits your certification
Simple
For companies certifying ISO 27001. Each risk is documented with its attributes, affected security dimensions, evaluation, treatment and safeguards.
Advanced
For ENS Medium or High category, or an ISMS that has been running for years. Each scenario links to threats and vulnerabilities from the ISO 27005 catalogue, and the platform ranks the most frequent ones across your register.
Your Qalea team helps you choose the methodology when you set up risk management.
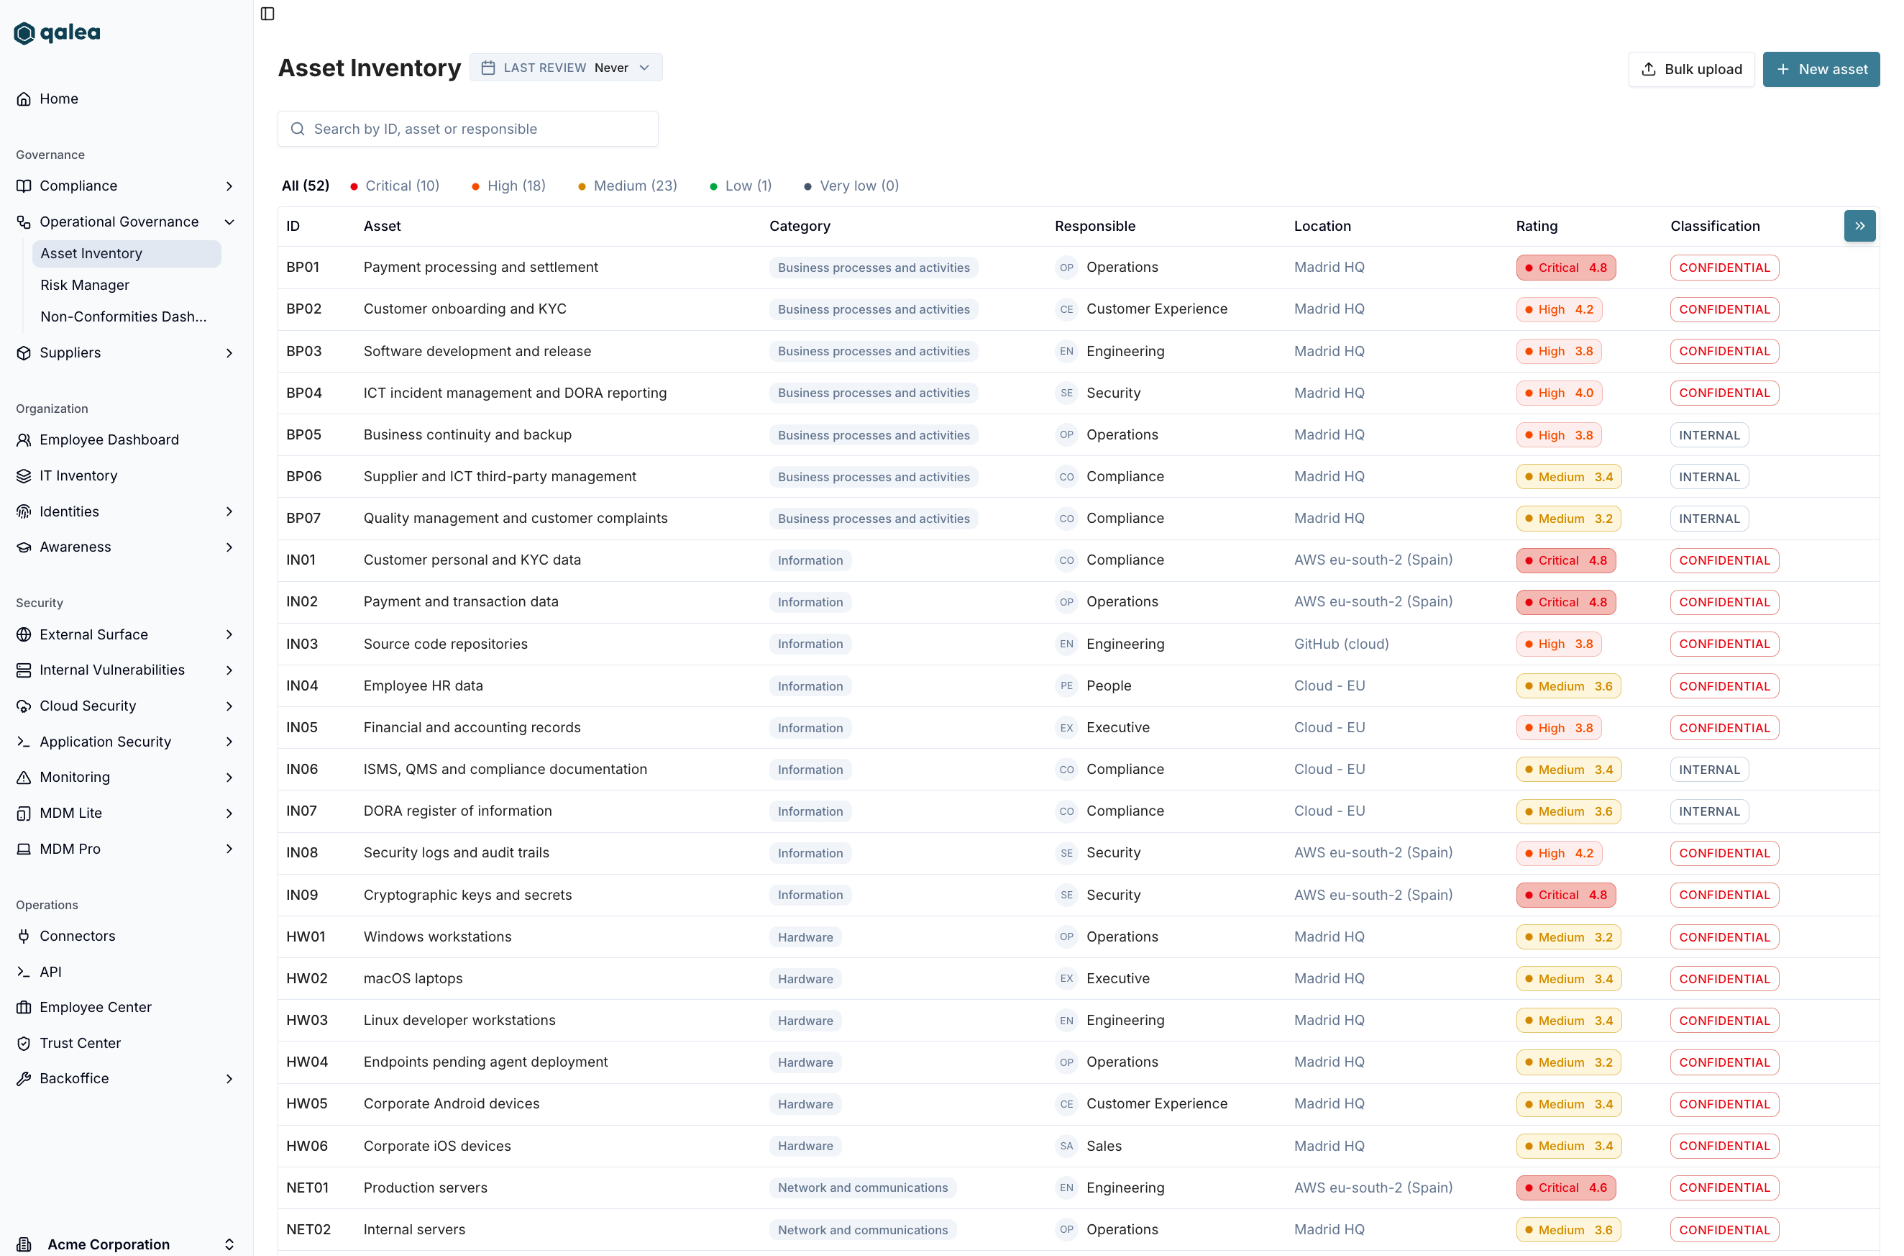
Asset inventory
Every asset has a responsible team, a location, a criticality rating and a classification.
Import assets in bulk, link them to the risks that affect them and record each review.
What each framework asks for

ISO 27001
Risk assessment and treatment (clauses 6.1.2 and 6.1.3), plus an inventory of information and other associated assets (Annex A 5.9).
ENS
Risk analysis (op.pl.1) and asset inventory (op.exp.1).

NIS2
Policies on risk analysis and information system security (Article 21).

DORA
An ICT risk management framework and the identification of ICT assets (Articles 6 and 8).
Risk management questions, answered
Keep learning about risk management



