The short version
Vanta and Drata are the two names most compliance shortlists come down to, and for good reason. Both replace the manual grind of evidence collection with software that connects to your cloud, identity and code systems and keeps you continuously audit-ready. They are close enough that choosing between them is a question of fit, not category: independent reviewers tend to conclude that both are excellent and that the right answer depends on who owns compliance inside your company.
Qalea belongs on the same shortlist for one kind of buyer and not another, and it is worth being plain about which. It is not a lighter or cheaper Vanta. It is a different model: the compliance platform and the security function that operates the controls, run together, and built for the Spanish and European frameworks, including ENS, that the US platforms do not carry. If your requirement is a self-served SOC 2 for US customers and you already have people to run your security, Vanta and Drata are built for exactly that buyer.
The three at a glance
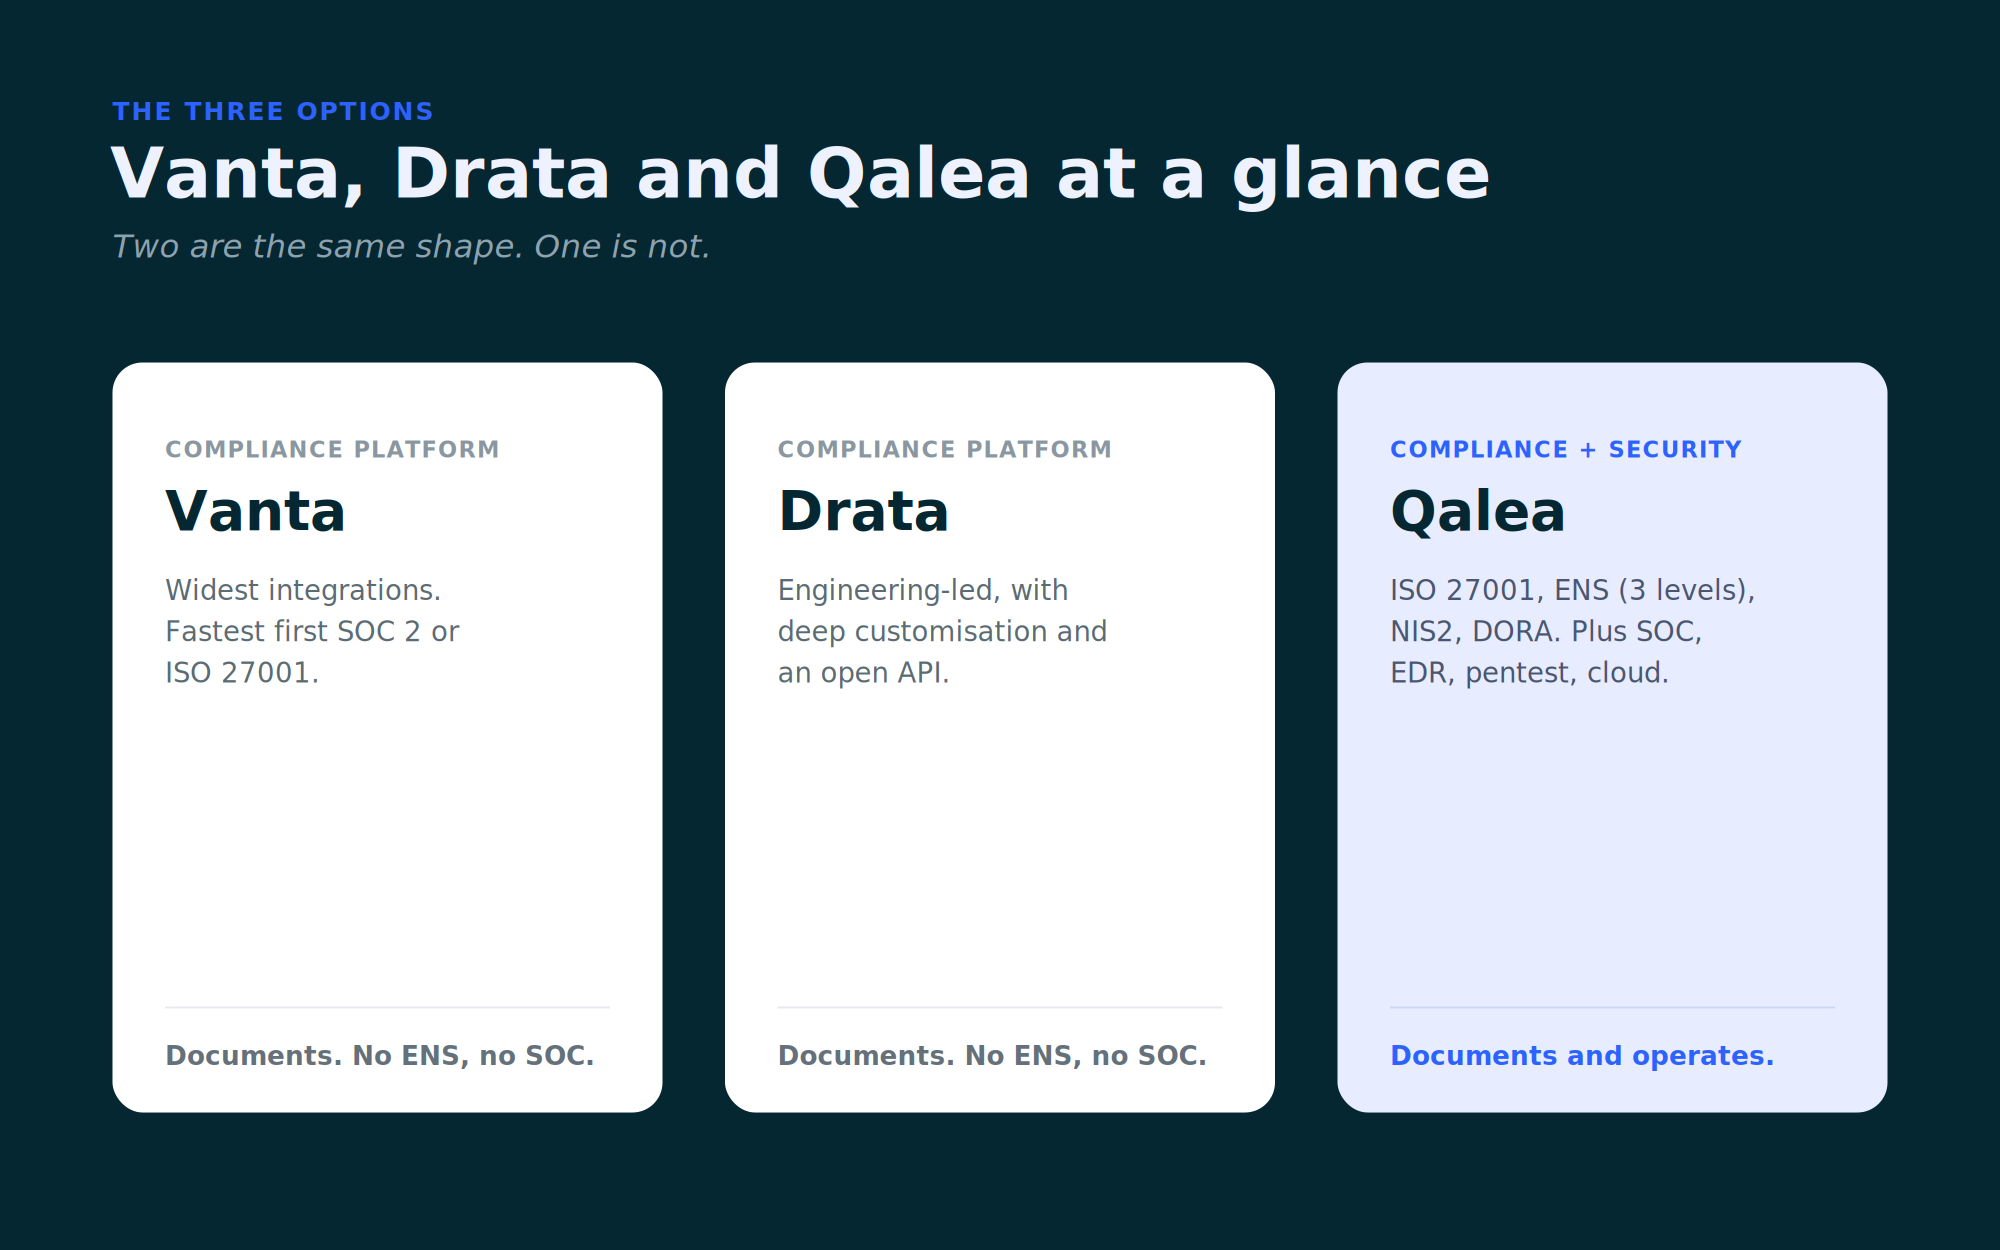
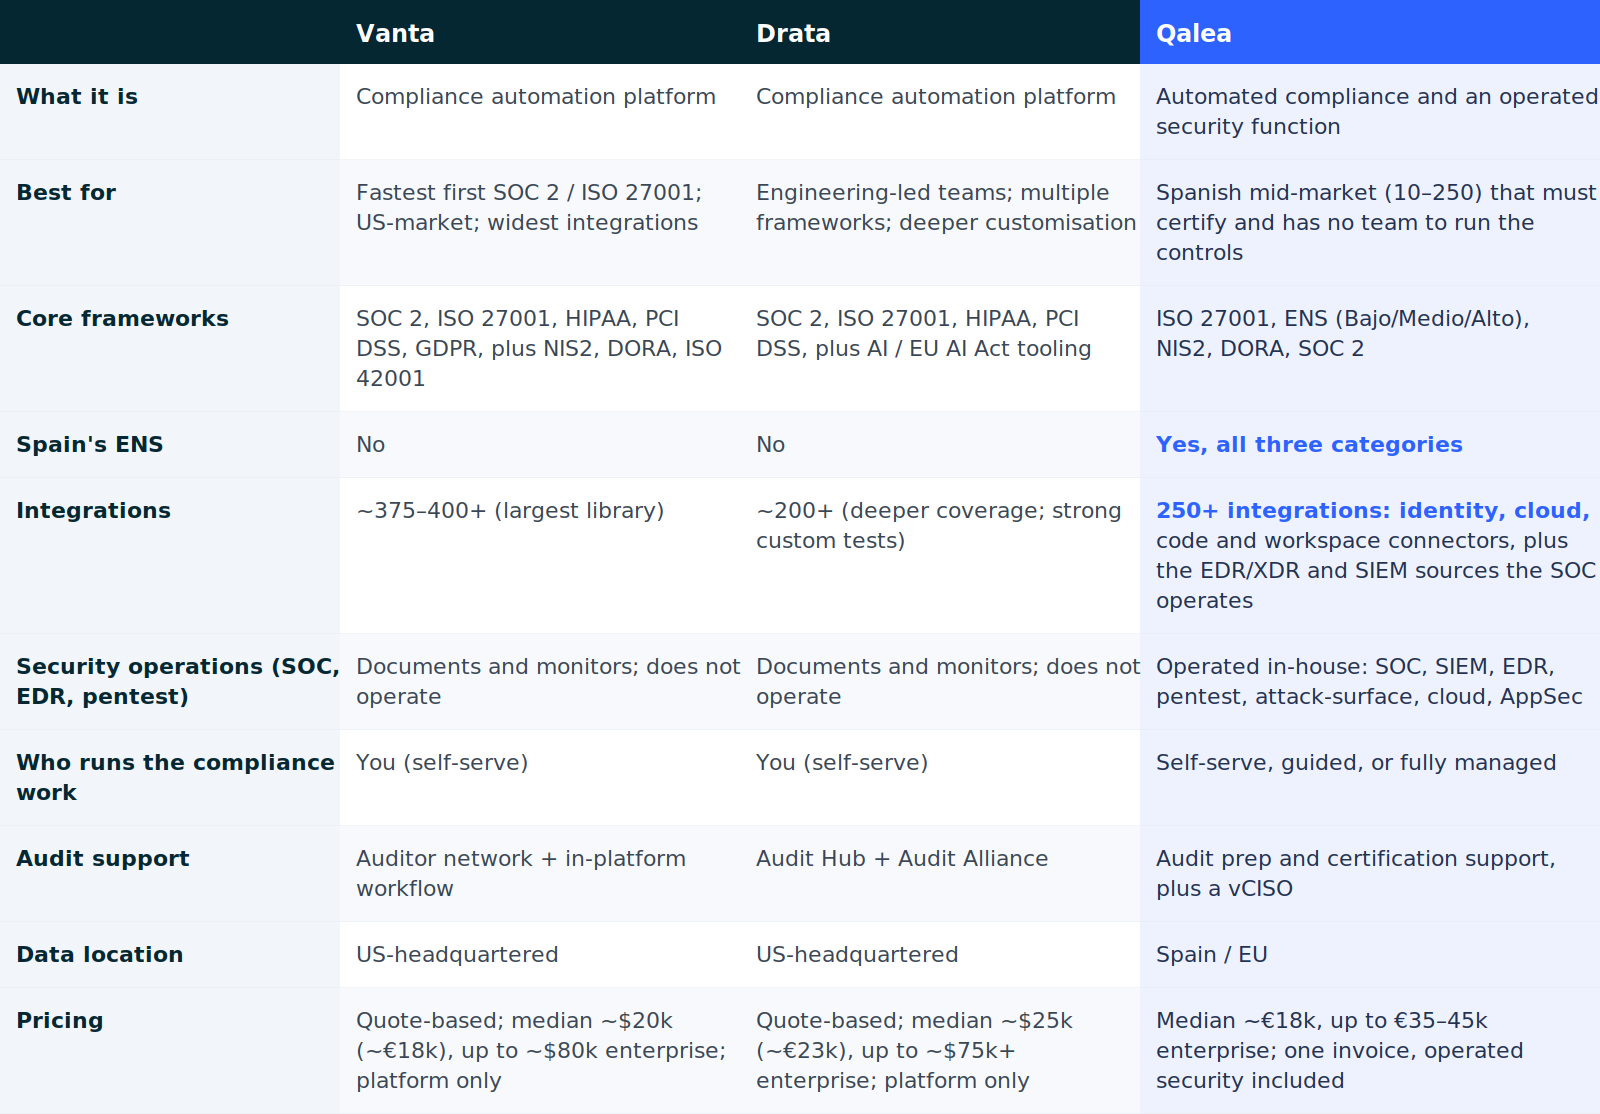
The two platforms are the same kind of tool; Qalea is a different shape. On the things that actually decide it, framework coverage including ENS, whether security is operated or only documented, and price, here is how the three line up.
What each costs. Neither Vanta nor Drata publishes a list price; both quote on headcount, framework count and add-on modules, and neither offers a free trial. In independent procurement data from Vendr, median annual spend is about $20,000 a year for Vanta and $25,000 for Drata, roughly €18,000 to €23,000, and it climbs steeply with size: ComplyJet reports that at the enterprise end platform spend reaches around $80,000 a year, before audits, implementation and per-framework fees (about $5,000 each) are added on top. And that buys the documentation platform alone, for a framework or two, with the SOC, the scanning, the penetration test and the vCISO still to purchase and staff separately. Qalea folds all of that into one service: it covers more of the frameworks a Spanish company needs, ISO 27001, ENS and the rest, and operates the security underneath them. Its median lands around €18,000, in the same band as the platforms' documentation-only median, and an enterprise programme runs about €35,000 to €45,000, roughly half what the platforms reach at that end, with the operated security included rather than assembled separately. Treat every figure here as a range, not a quote: the only number that holds is the one on your own proposal.
Vanta vs Drata: the real differences
Both platforms solve the same core problem, so the differences are about shade and shape rather than whether they work.
Integration breadth is Vanta's clearest advantage. It carries the largest connector library on the market (around 375 to 400 integrations, against roughly 200 for Drata) and runs a high-frequency automated test cadence, which means a standard cloud-native stack (AWS or GCP, Okta or Google Workspace, GitHub, Jira, a common HRIS) is largely covered out of the box. If your stack includes something niche, Vanta is the more likely to have a native connector rather than a manual upload.
Customisation and depth are Drata's. Its integration list is smaller but tends to go deeper on what it supports, and its custom-tests framework and open API make it the more comfortable choice for an engineering-led team that wants to model its own controls rather than work inside fixed templates. Its Audit Hub lets the auditor work inside the platform, and Audit Alliance is its own directory of partner audit firms.
Stage is the practical dividing line. Vanta is often adopted by companies preparing a first SOC 2 or ISO 27001 that value its template library and auditor familiarity. Drata is more often adopted by companies managing several frameworks at once, where its per-control automation reduces repeated evidence work.
Pricing is close and opaque on both sides. Neither publishes a list price; both quote on headcount, framework count and add-on modules such as vendor-risk management or a trust centre, and both commonly ask for multi-year commitments. Reported medians sit within a few thousand dollars of each other, so price rarely decides this on its own.
The fair summary is the one most independent comparisons reach: both are strong, and the choice turns on who owns compliance in your company and how much you want to customise.
What both leave to you
This is the part that matters most for a European buyer, and it is not a criticism of either product. It is what compliance automation is, by design.
A platform automates the documentation. It maps controls, keeps your Statement of Applicability and risk register current, and collects the evidence an auditor reviews. What it does not do is operate the security those controls describe. When a control has to actually work, when a client sends a security questionnaire, or when an alert fires at two in the morning, the software has nothing to say. Someone still has to interpret findings, drive remediation, run the penetration test, own the policies and answer the questionnaire. Independent reviewers put that at a part-time job of several hours a week at minimum, and often a full-time role once you pass a hundred people. In budget terms, the platform is one line item; the security function it assumes, the SOC, the EDR, the scanning, the awareness training and the penetration test, is a separate stack you buy and staff on top of it.
So a company with no internal security team can buy the best platform on the market and still arrive at the audit with a complete evidence pack sitting on top of controls that nobody operates. The certificate is not won by the pack; it is won by the function underneath it.
Two more gaps matter specifically in Spain. Neither Vanta nor Drata carries ENS, the Spanish scheme under Real Decreto 311/2022 with its own CCN control catalogue, which international platforms have not built for. And both are US-headquartered, so data residency is a fair question to put on the demo if your buyers or regulators care where compliance data is processed.
Where Qalea fits, and where it does not
Qalea is built for the buyer those gaps describe: a Spanish company that has to certify and does not have a security team to run the controls a platform documents.
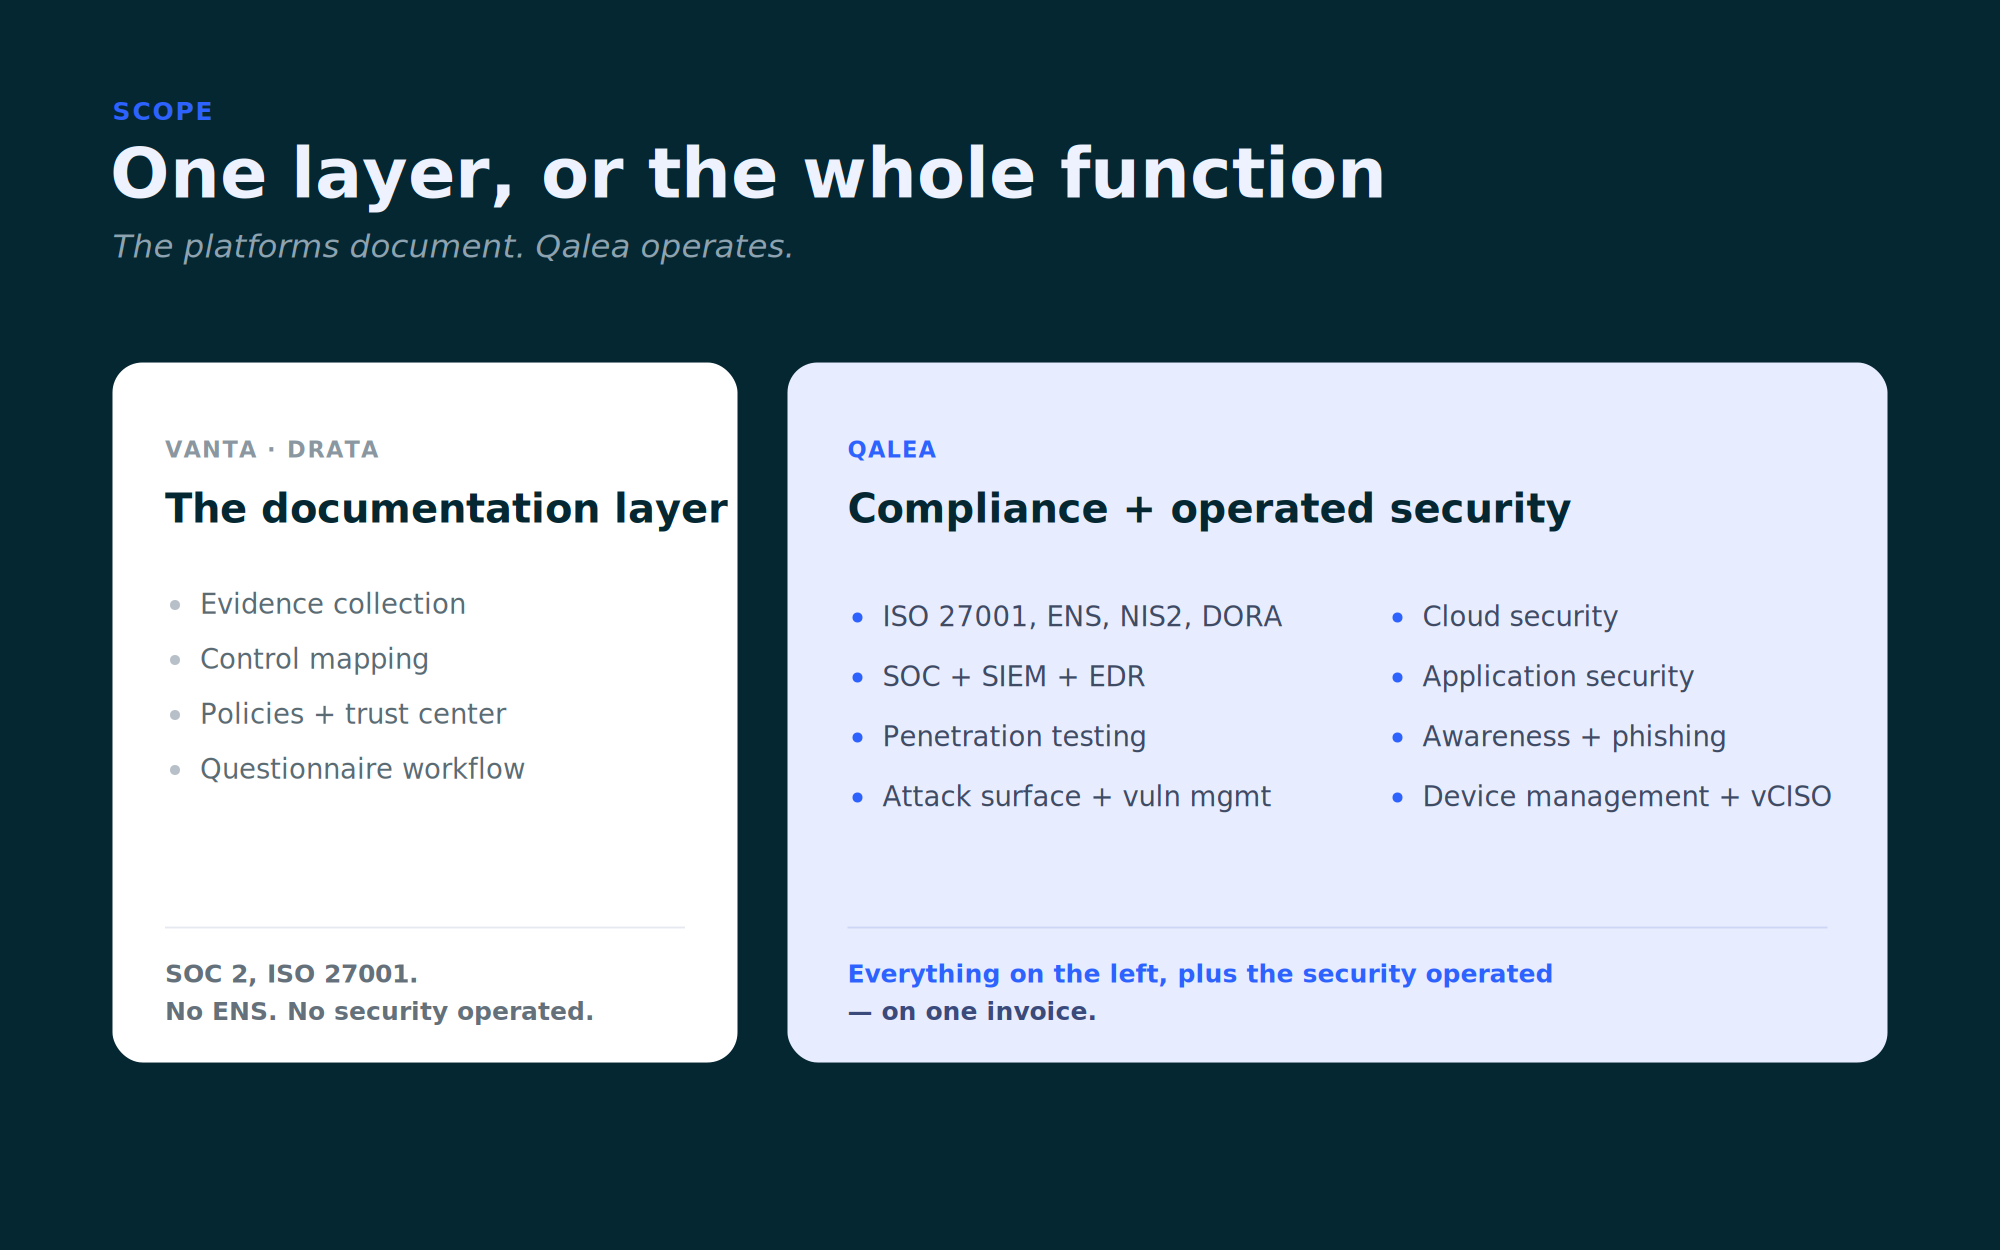
It runs the same kind of automated compliance platform, a digital ISMS for ISO 27001, ENS, NIS2, DORA and SOC 2 with evidence collection, risk and supplier management and a continuously audit-ready state. Underneath it, and this is the difference, it operates the security: an in-house SOC with SIEM and EDR across laptops and servers, external attack-surface and internal vulnerability management, cloud misconfiguration monitoring on AWS, GCP and Azure, application security from commit to runtime, a manual penetration test, plus phishing-based awareness and device management, with a vCISO for the architecture and questionnaire judgement a platform cannot provide. It covers ENS at all three categories, and it delivers this on a spectrum from self-serve to fully managed, sized for a company of ten to two hundred and fifty. It is billed as one tiered service rather than a per-seat licence, so a company without an internal team is comparing it not against a single licence but against the SOC, the scanning, the penetration test and the vCISO it would otherwise assemble and staff separately. Its median programme lands around €18,000 a year, the same band as a documentation platform alone, and an enterprise programme runs about €35,000 to €45,000, roughly half what the platforms reach at enterprise scale, with the operated security and the Spanish frameworks included rather than assembled separately. Qalea helps companies become audit-ready and runs the security that keeps a certificate valid.
The honest boundaries matter as much as the fit. Qalea is not a two-hundred-framework catalogue; it covers the frameworks a Spanish mid-market company has to certify and operates the security underneath them, rather than documenting many frameworks shallowly. If your requirement today is HIPAA, TISAX or a US-first SOC 2 with your own team already in place, that is the buyer Vanta and Drata are built for.
Who each is built for
The fit depends on your situation more than on the brand.
- SOC 2 first, selling to US customers, security already staffed: this is the buyer global automation platforms are built for. Vanta brings the widest integration library; Drata brings deeper customisation and multi-framework work.
- ISO 27001 for European customers, no ENS, security run in-house: both platforms cover this; EU data residency and the exact frameworks in scope are the questions that separate them.
- ISO 27001 or ENS, with no internal team to operate the controls: this needs Spanish framework coverage and operated security in one place. That is the narrow set Qalea is built for; a global tool leaves the SOC, the pentest and the vCISO to be assembled separately.
Whatever you shortlist, ask three questions on the demo: does it cover ENS at the category my tenders require; is any security operation included, or is that my job; and where is my compliance data processed. The answers separate these three in minutes.
See the full market map, including the Spanish security providers and ENS specialists, in Best Compliance Automation Platforms for Spain in 2026.